Bishita un konferensia internashonal di hacker
OWASP Global AppSec Amsterdam
- Publiká
- Aktualisá
- (kreá )
- Skirbí pa
- Willem L. Middelkoop
- Tópikonan
- Amsterdam · Nintendo · sibersiguridat · data · hacking · hende · trabou
- Vershon humano di e artíkulo aki
- https://willem.com/pap/2019-09-27_bishita-un-konferensia-internashonal-di-hacker/
- English
- Visiting an international hackers conference
- Nederlands
- Het bezoeken van een internationale hackersconferentie
- Deutsch
- Besuch einer internationalen Hackerkonferenz
- Español
- Visita a una conferencia internacional de hackers
- Français
- Visite d'une conférence internationale de hackers
- Italiano
- Visita a una conferenza internazionale di hacker
- Português
- Visitar uma conferência internacional de hackers
- Frysk
- In ynternasjonale hackerskonferinsje besykje
- Lenganan
- Tradusí for di e original ingles pa un modelo di lenga den dos rònde (traduksion i korekshon) ku un glosario i un kontròl di ortografia; ainda no lesá pa un lektor ku Papiamentu komo lenga mamá.
Resumen
Luna aki mi a tin e suerte di bai na Global AppSec Amsterdam, un konferensia internashonal pa hacker i spesialista di siguridat. Tabatin presentashon di ex-agente di inteligensia, kazador di bounty, akadémiko i bendedó di software. Mi a siña tokante algun di e téknikanan di hacking mas nobo, mi a topa hende interesante i mi a wega algun wega retro kool. Lesa mas aki bou.
Teksto kompleto
OWASP Foundation i Global AppSec Amsterdam
E OWASP Foundation ta un organisashon sin fin di lukro ku ta dediká na krea herment, dokumentashon, foro i konferensia tokante siguridat di software. OWASP ta spesial pasobra e ta liber di presion komersial, e no ta afiliá ku ningun kompania di teknologia. Nan ta aboga pa trata siguridat di aplikashon komo un problema di hende, proseso i teknologia, pasobra e manera mas efektivo pa siguridat di aplikashon ta inkluí mehoramentu den tur e áreanan aki. Bo por haña mas tokante OWASP riba https://www.owasp.org.
E eventonan Global AppSec ta wòrdu organisá rònt mundu. Sèptèmber aki tabatin un evento asina den mi stad natal Amsterdam. Chèk nan kalènder pa haña si OWASP ta bini na bo stad.
Ora siguridat sibernétiko ta bira real: Squashing Terrorists
Unu di e historia mas impresionante a wòrdu kontá pa Chris Kubecka, un muhé ku a traha pa e Air Force di Merka i United States Space Command. E ta investigadó di siguridat di kompiuter i spesialista den guera sibernétiko.
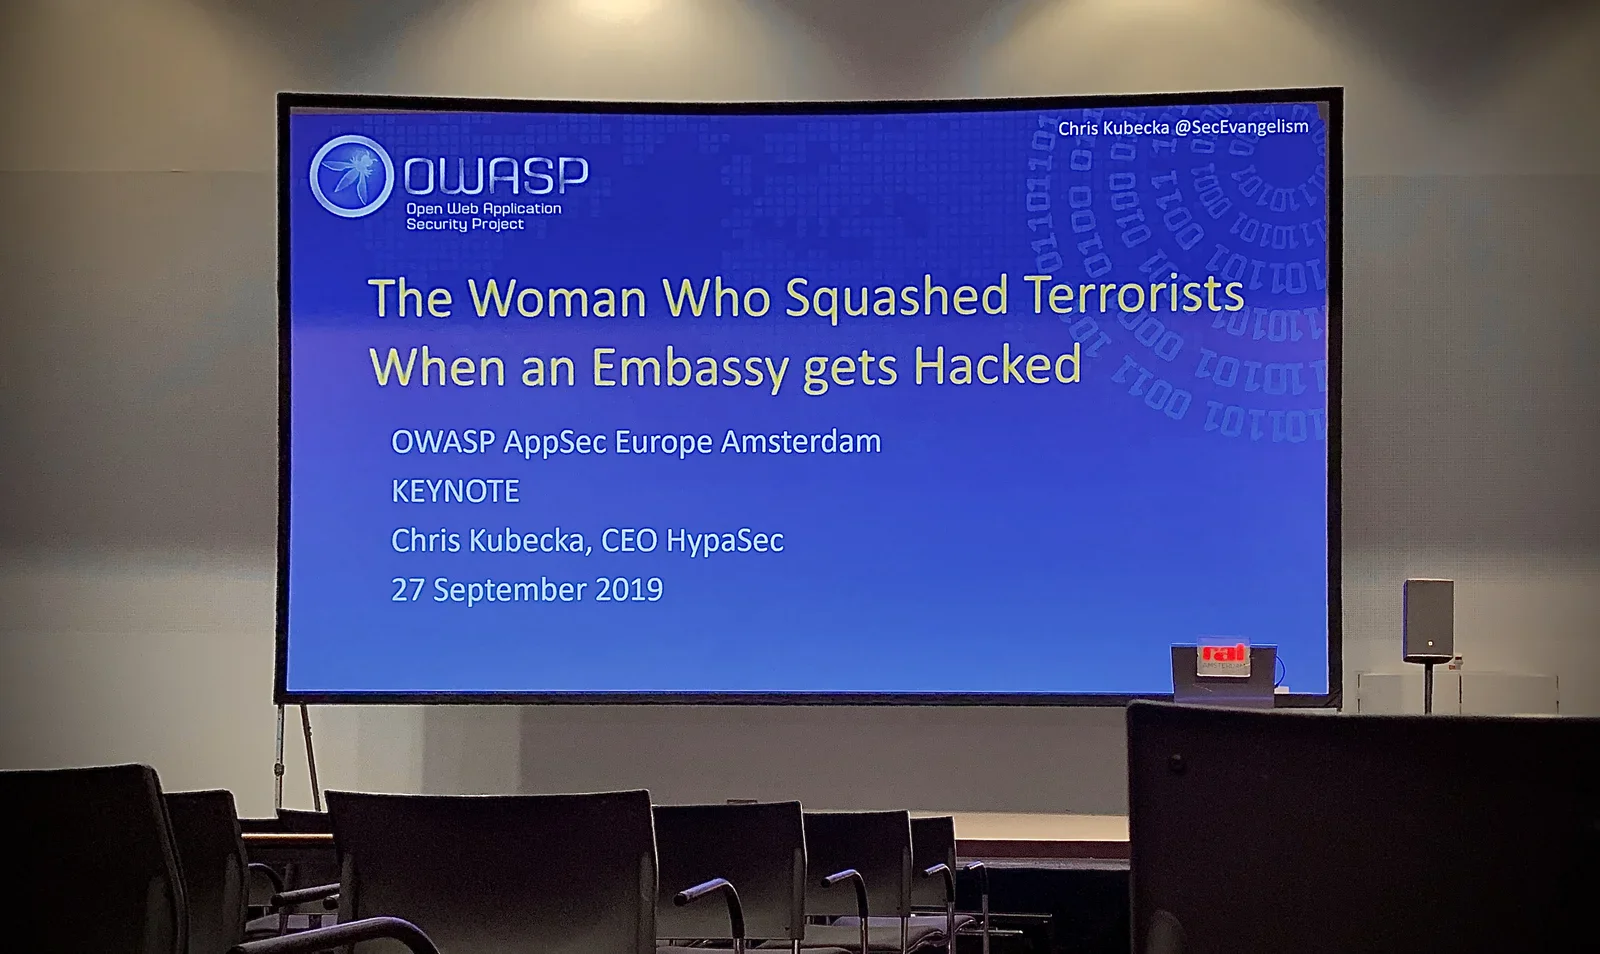
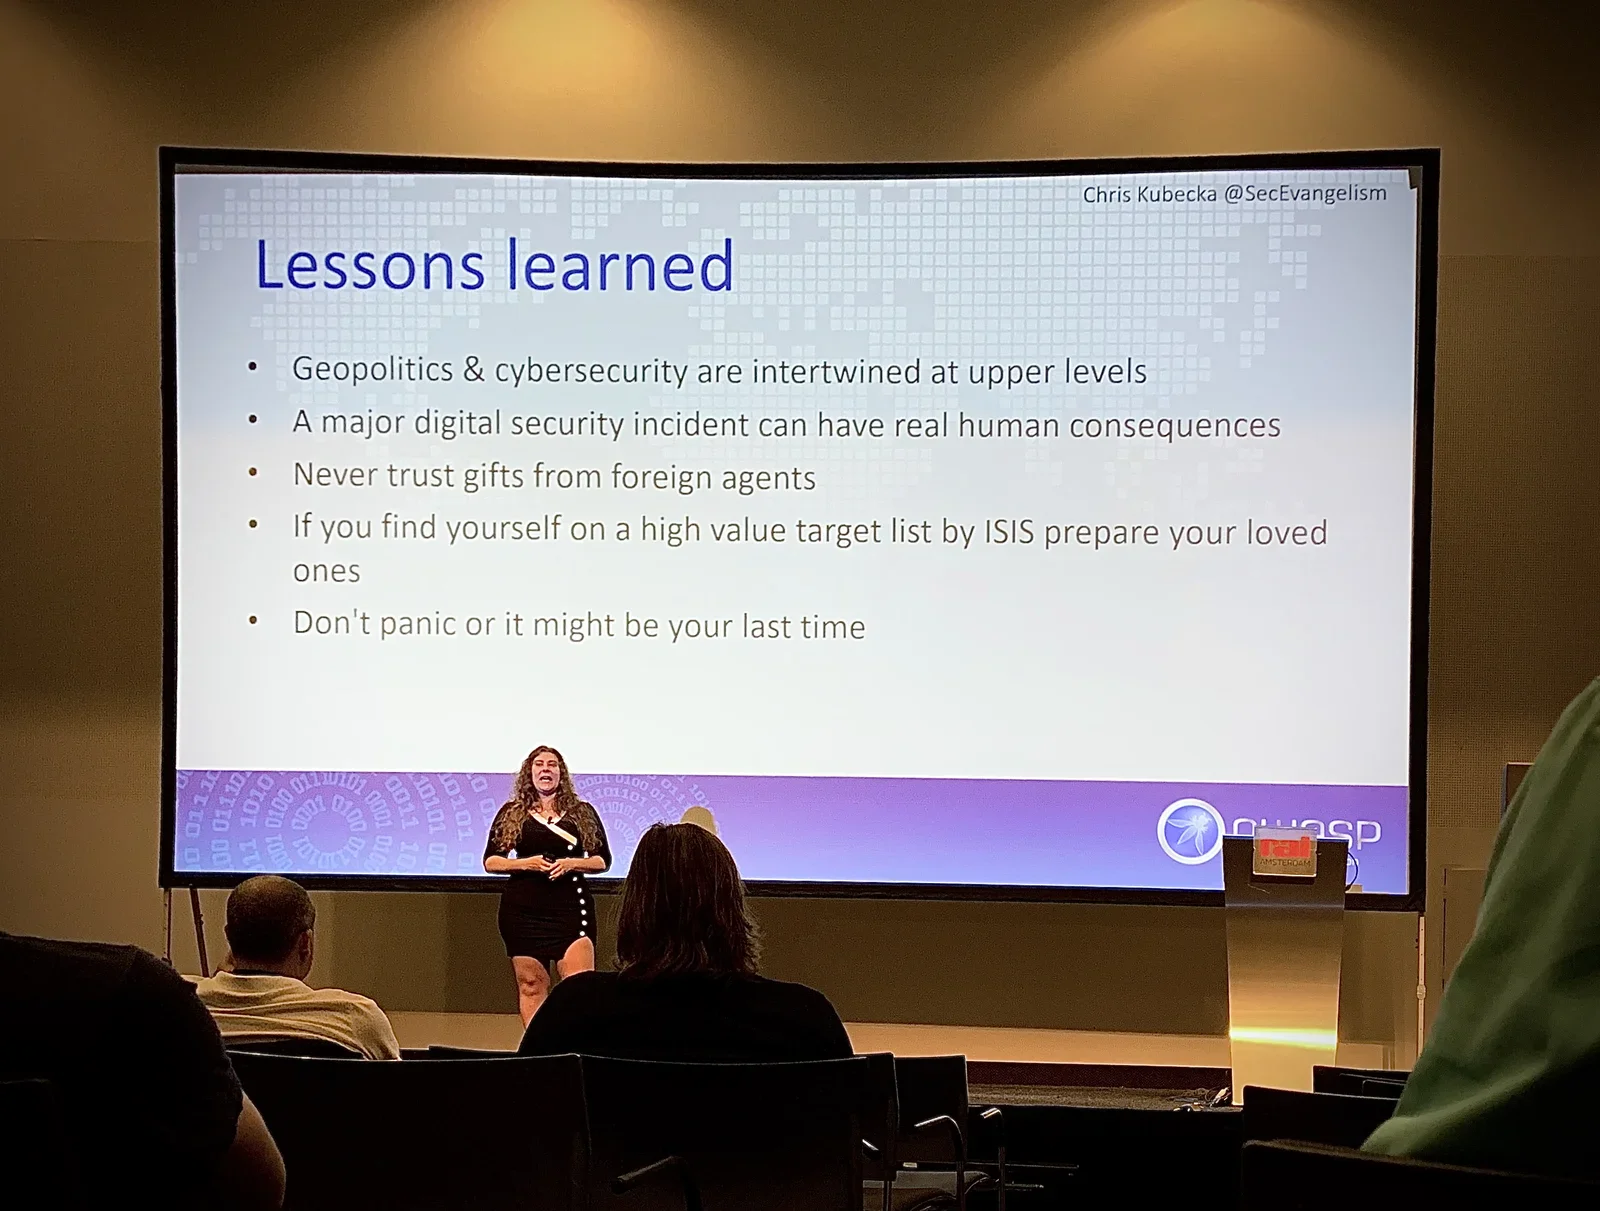
E ta konta tokante su trabou na e Embahada Real di Arabia Saudita na Den Haag. Ta hopi interesante pa siña kon polis lokal, e Korpo Diplomátiko i agente spesial a wòrdu involukrá pa na final prevení un atake ku bom riba e Kurhaus na Scheveningen. Ta ora bo tende e historianan aki ku bo realisá ku no tur kos ku pasa ta sali den e notisia!
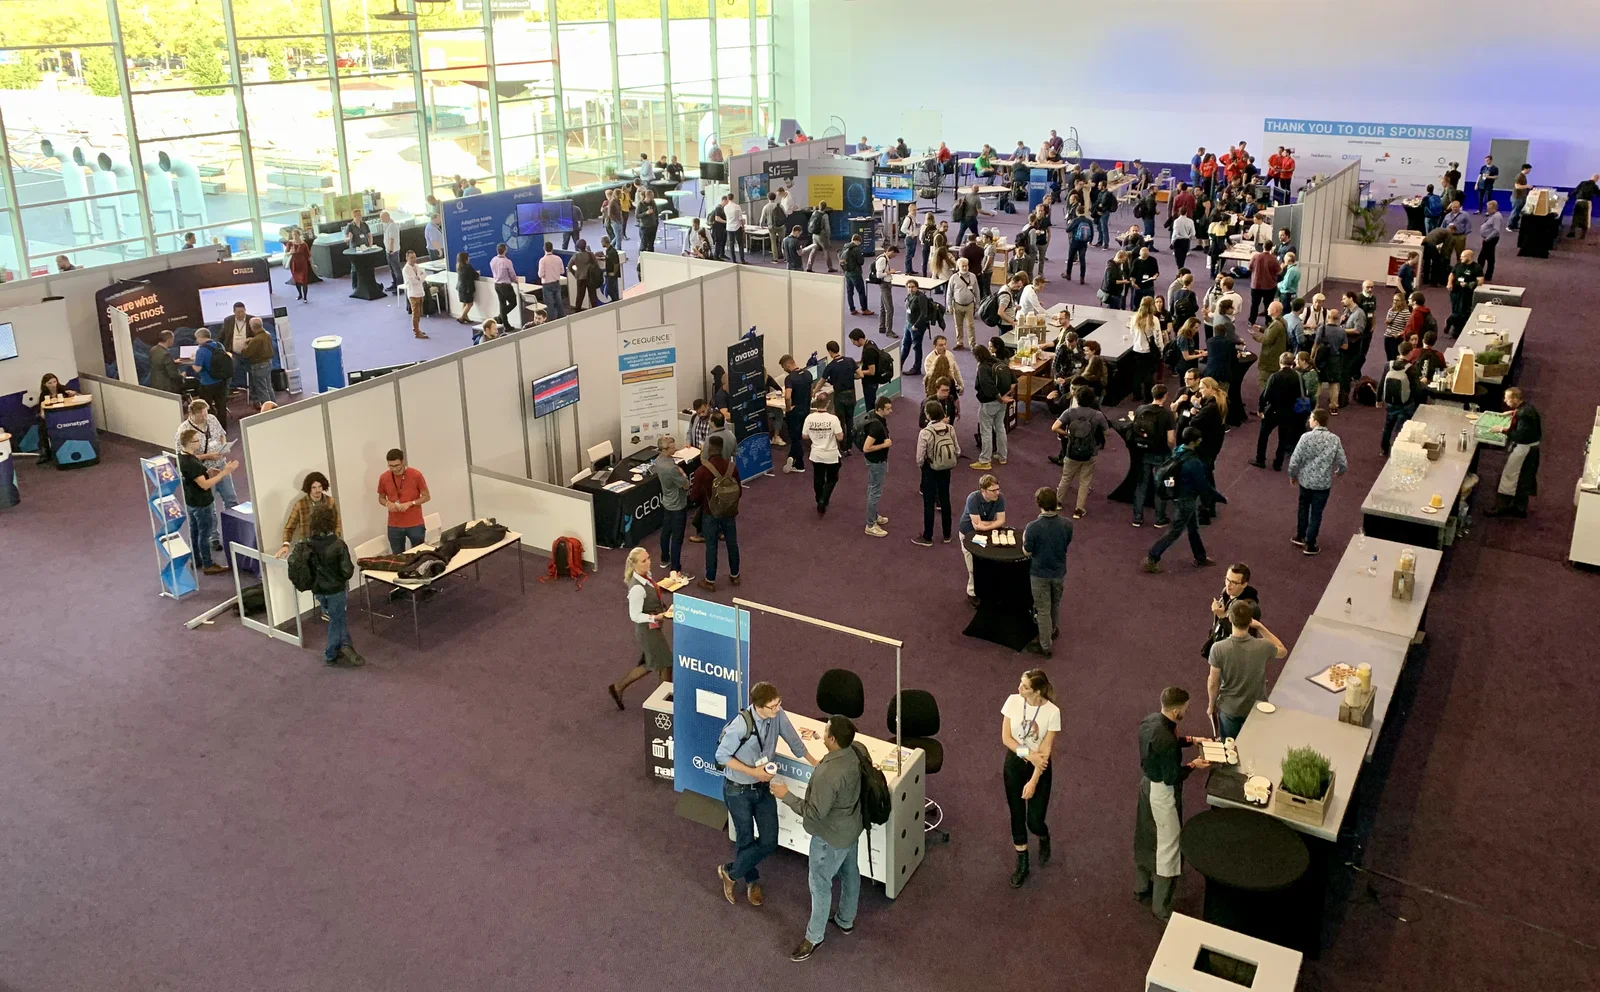
Kòfi i wega
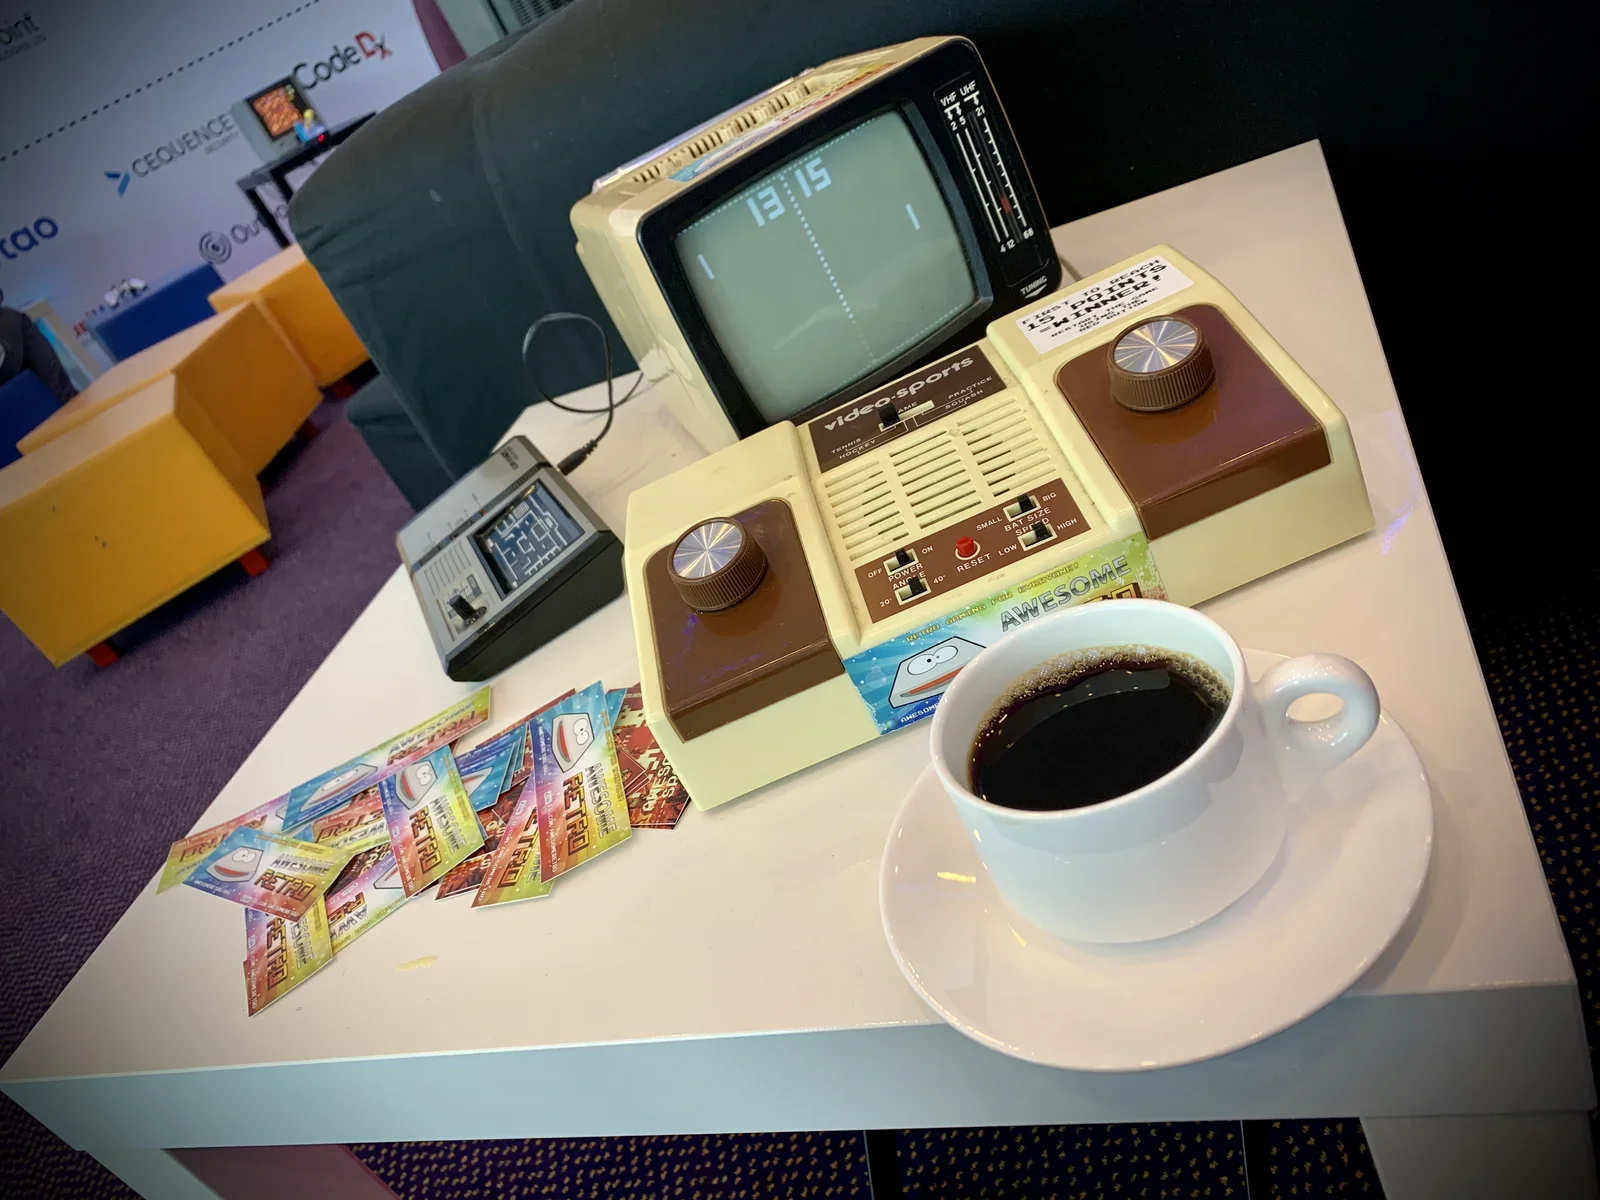
Despues di e keynote tokante terorista, guera sibernétiko i atake ku bom, ora a yega pa un kòfi i algun wega. Wega wega retro ta un manera divertido pa konosé otro hacker na e konferensia, pasobra bo tin algu obvio na komun pa papia dje. Esei ta útil, pasobra mayoria di e ekspertonan di IT mester di un tiki yudansa pa kibra e yelo ora ta trata di sosialisá...
Téknikanan di hacking
Despues di kòfi tabatin diferente seshon ku bo por a bai na dje. Mi a skohe algun basá riba mi interes personal i mi trabou.
Persistent Client-Side XSS
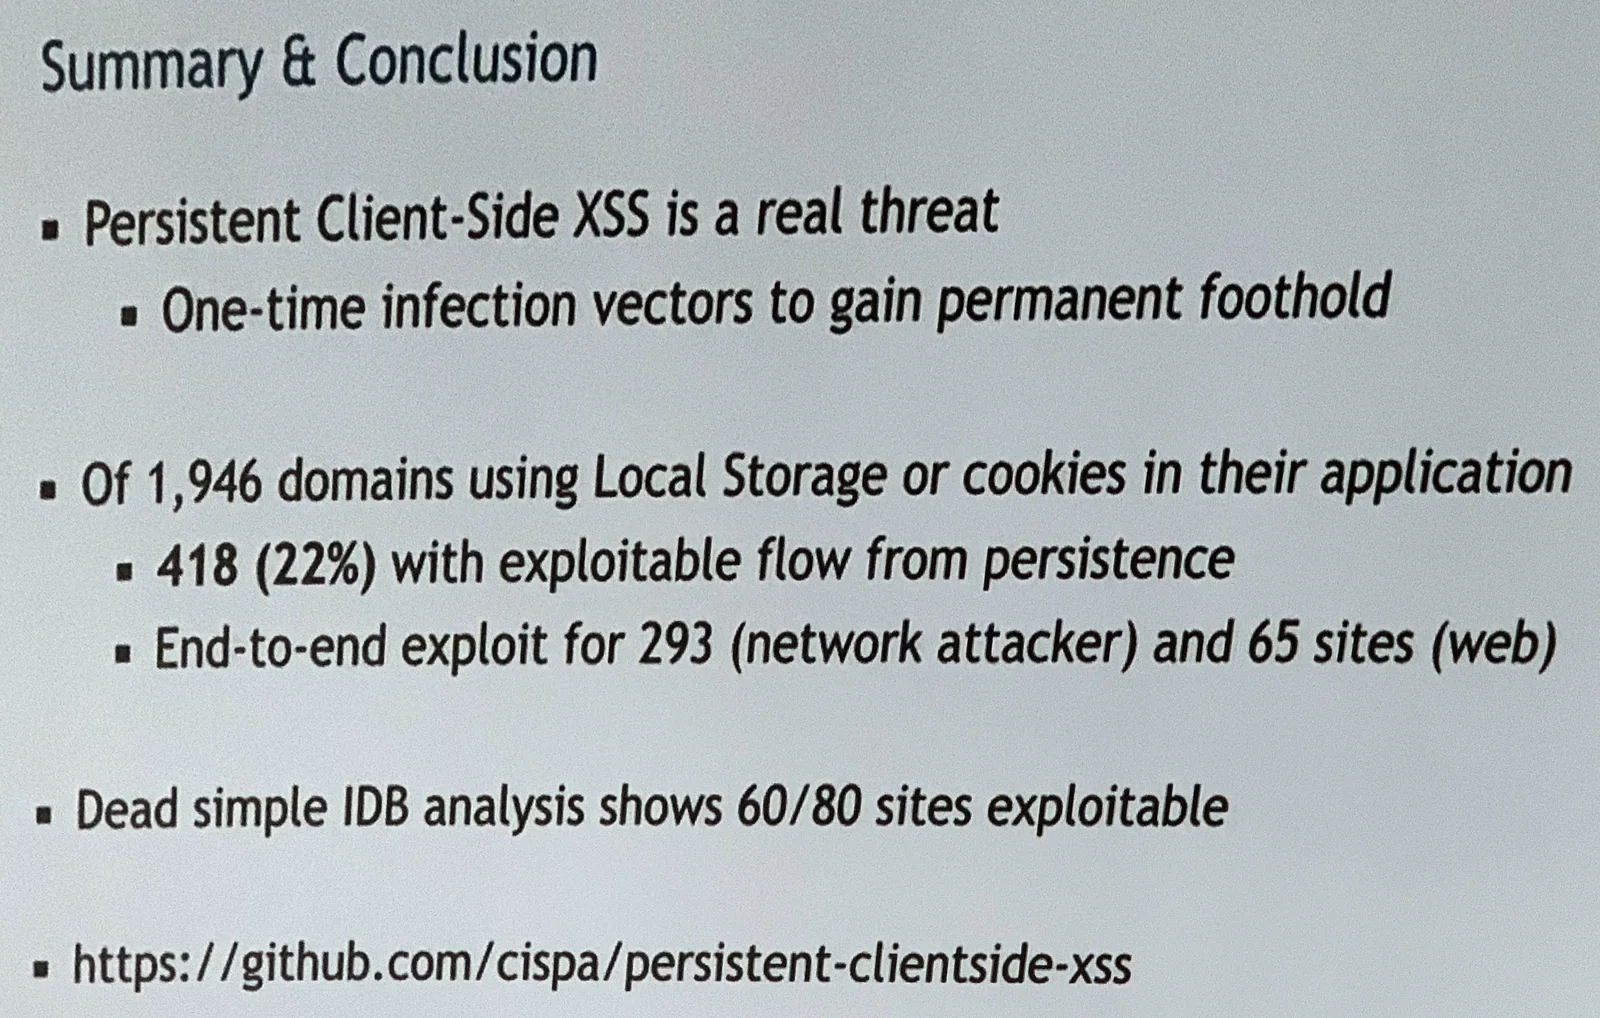
Unu di e presentashonnan ku mi a asistí tabata tokante atake riba website ku ta usa Local Storage of cookie. Ku e nòmber apropiá "Don't trust the locals", e presentashon di Marius Steffens i Ben Stock tabata hopi interesante. Nan investigashon akadémiko a revelá ku hopi website ta vulnerabel pa amenasa ku ta haña un posishon permanente!
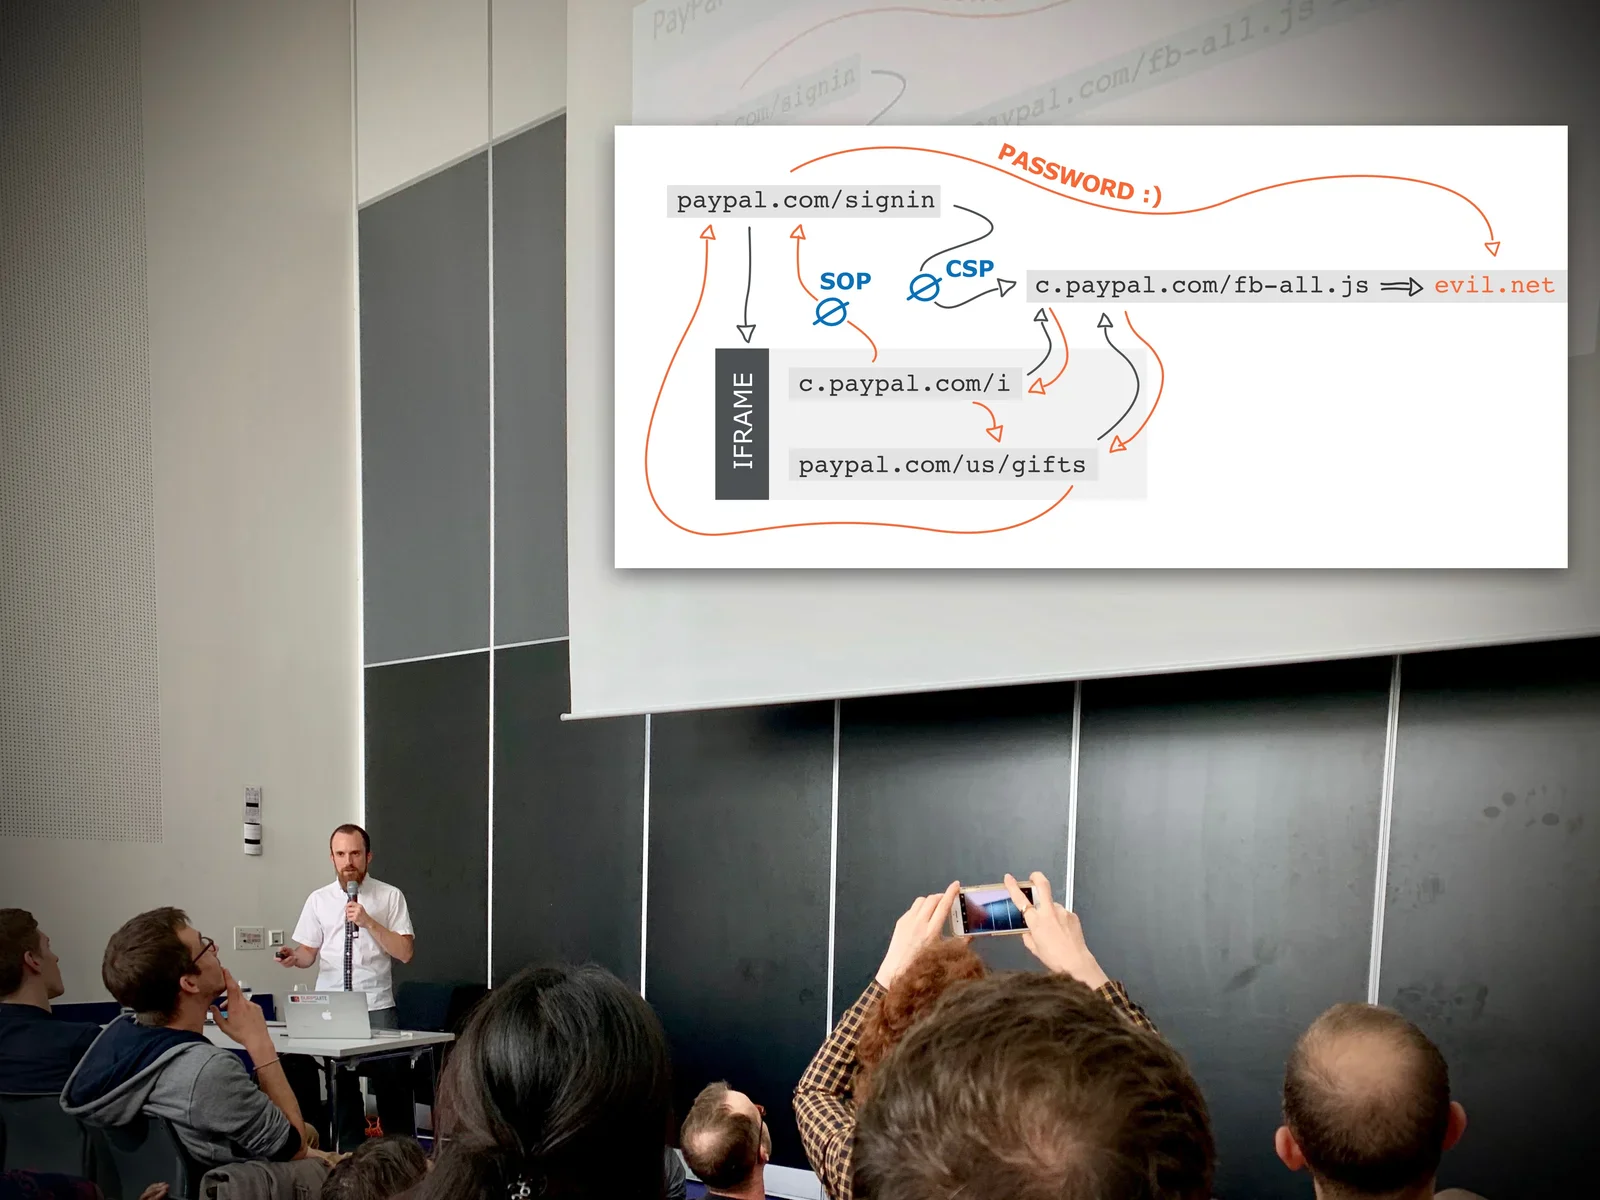
Hacking PayPal ku un atake HTTP desync
Den su presentashon brilante, James Kettle ta deskribí su investigashon tokante un di e téknikanan di hacking mas peligroso, probabel riba e web moderno: HTTP Request Smuggling dor di desinkronisá petishon HTTP. E téknika aki ta usa vulnerabilidat ora un website ta usa un content delivery network (CDN), un web cache of un web application firewall (WAF). Ta sorprendente pa siña tokante esaki, pa komprendé e prinsipio ku ta bou di dje i pa siña kon defendé kontra e tipo di atake aki.
Ekonomia di hacking: kuantu ta vale un kuenta hackeá?
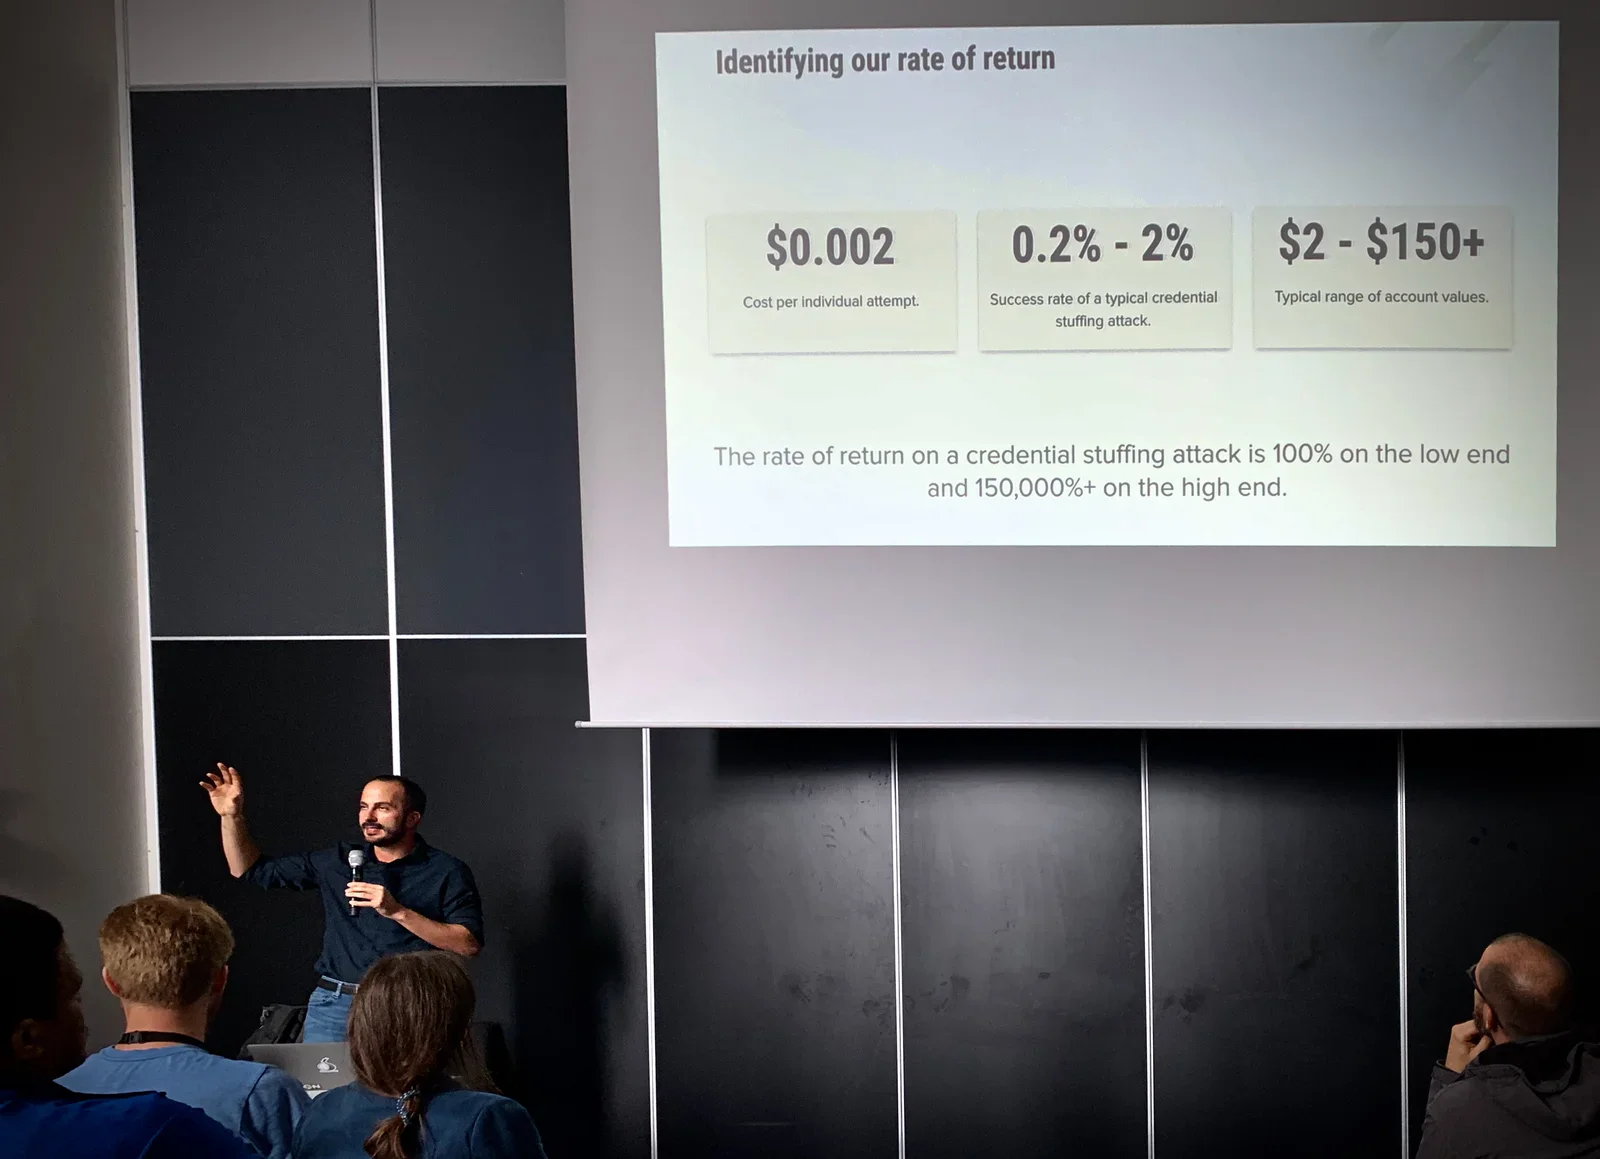
Den un otro presentashon interesante Jarrod Overson ta splika e situashon di atake di credential stuffing. E tipo di atake aki ta usa nòmber di kuenta i password ku a skapa, riba diferente website, loke ta hopi eksitoso (sorprendente), pasobra hopi hende ta usa e mes password riba diferente website. E ta splika kon pa evitá CAPTCHA i kon hacker ta hasi nan malware imitá kondukta humano pa fraude. E ta konkluí ku fraude ta un problema humano, no téknico, impulsá pa ekonomia simpel: ta vale e pena pa hack!
Mentalidat di hacker
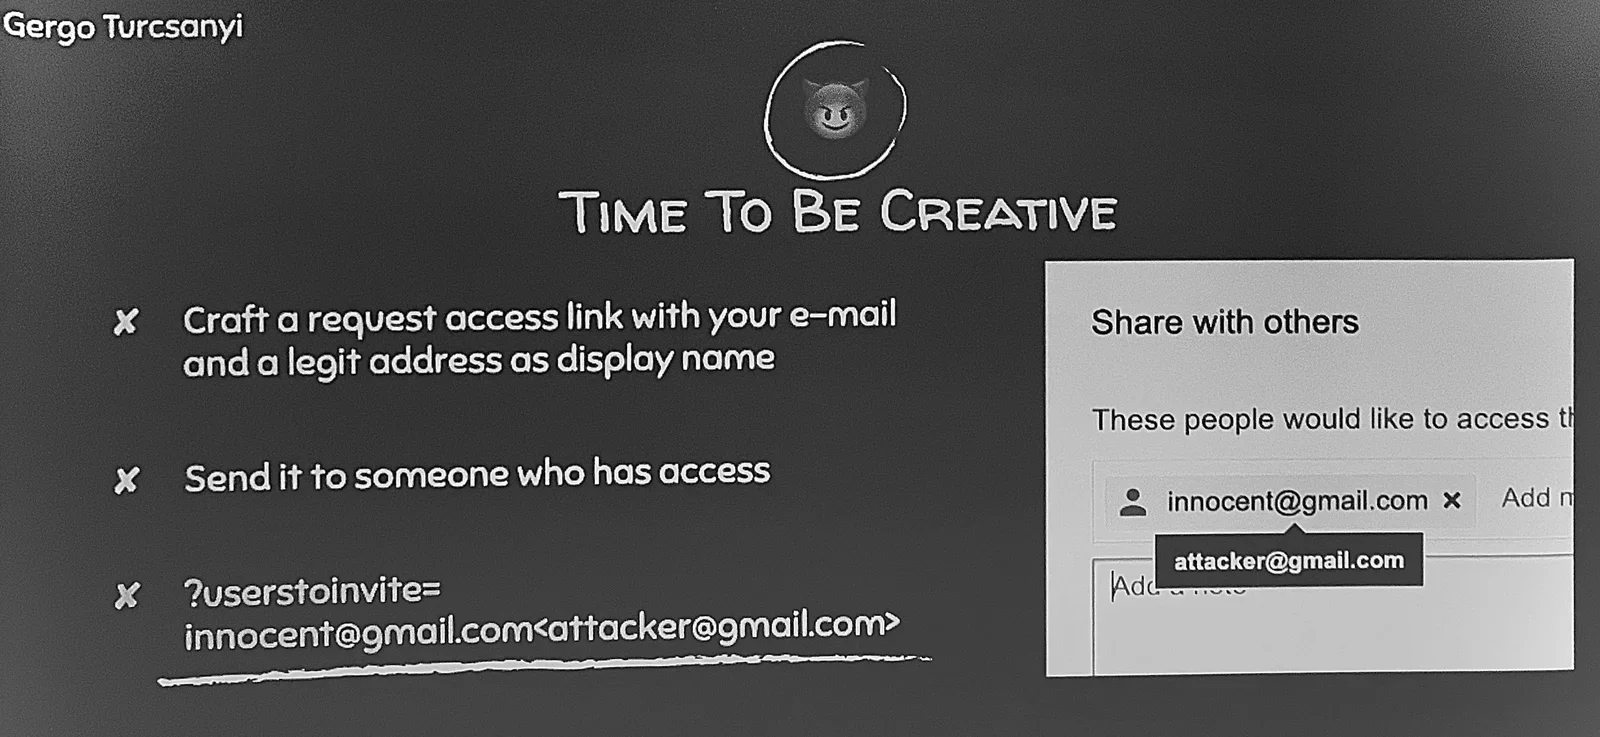
Den su presentashon, Gergö Turcsányi ta konta kon e a bira un kazador di bounty. E ta splika ku bo no mester ta un matemátiko hopi bon pa hasi esaki, tur loke bo mester ta un poko kreatividat i tempu pa hurga rònt di tempu na tempu. Na final esaki a hiba e pa hack Google ku éksito!
Konklushon
Bishitá Global AppSec tabata fantástiko! Ta un privilegio pa konosé otro hacker, siña di nan i tende tokante kosnan ku mayoria di biaha bo no ta mira den e notisia.
Kiko ku bo tuma ku bo for di un konferensia, semper lo tin algu ku bo no tabata spera pa siña. Ta e siñamentu inesperá aki ku ta hasi bishitá konferensia vale e trabou hopi!